[ARC 2.1] Build Sheet: Onboarding at Scale
The build companion to the onboarding article: the low-power onboarding identity, the connectivity choice, agent hardening, and the verification that proves a server is genuinely managed.


The build companion to the onboarding article: the low-power onboarding identity, the connectivity choice, agent hardening, and the verification that proves a server is genuinely managed.
Onboarding a server to Arc looks like an install step. It is really a grant of code execution and a network-path decision, and the defaults do not make either choice for you.
Arc extends Azure’s management plane onto servers Azure does not host. The control plane is free, the management meters, and your Windows Server licensing decides which.
The build for standing up the identity sensor estate, both generations, from an empty tenant to a fabric that audits itself and is proven to deliver a detection into the queue.
The cheapest identity attack to survive is the one your configuration never left open. The standing assessments, the honest account of what became of lateral movement paths, and an order that reflects the attacker.
A detection is only half a control. The other half is what you can do the moment it fires, which on this product is two different surfaces people run together at their peril.
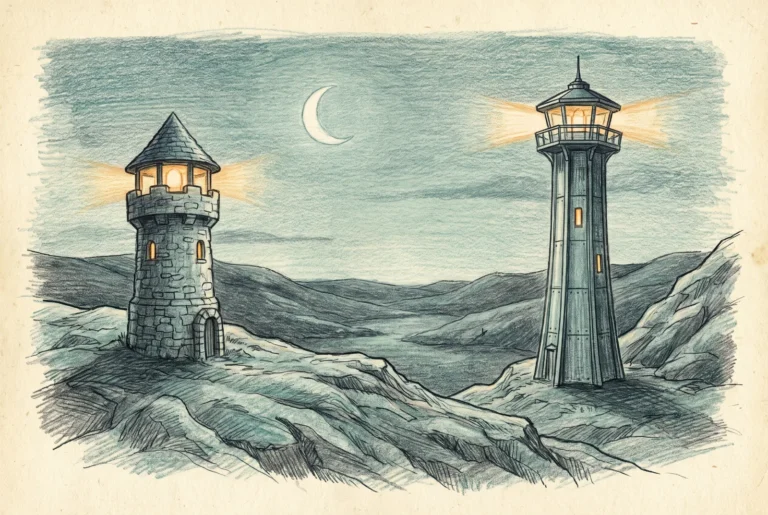
You will run two generations of the identity sensor at once, and that is the supported steady state. Which machine belongs to which generation, and why the new one breaks habits carried from the old.
Defender for Identity is no longer the on-premises member of the suite. It has two ends now, a sensor fleet on the identity fabric and the cloud directory itself, and the licensing carries a question nobody has answered.



